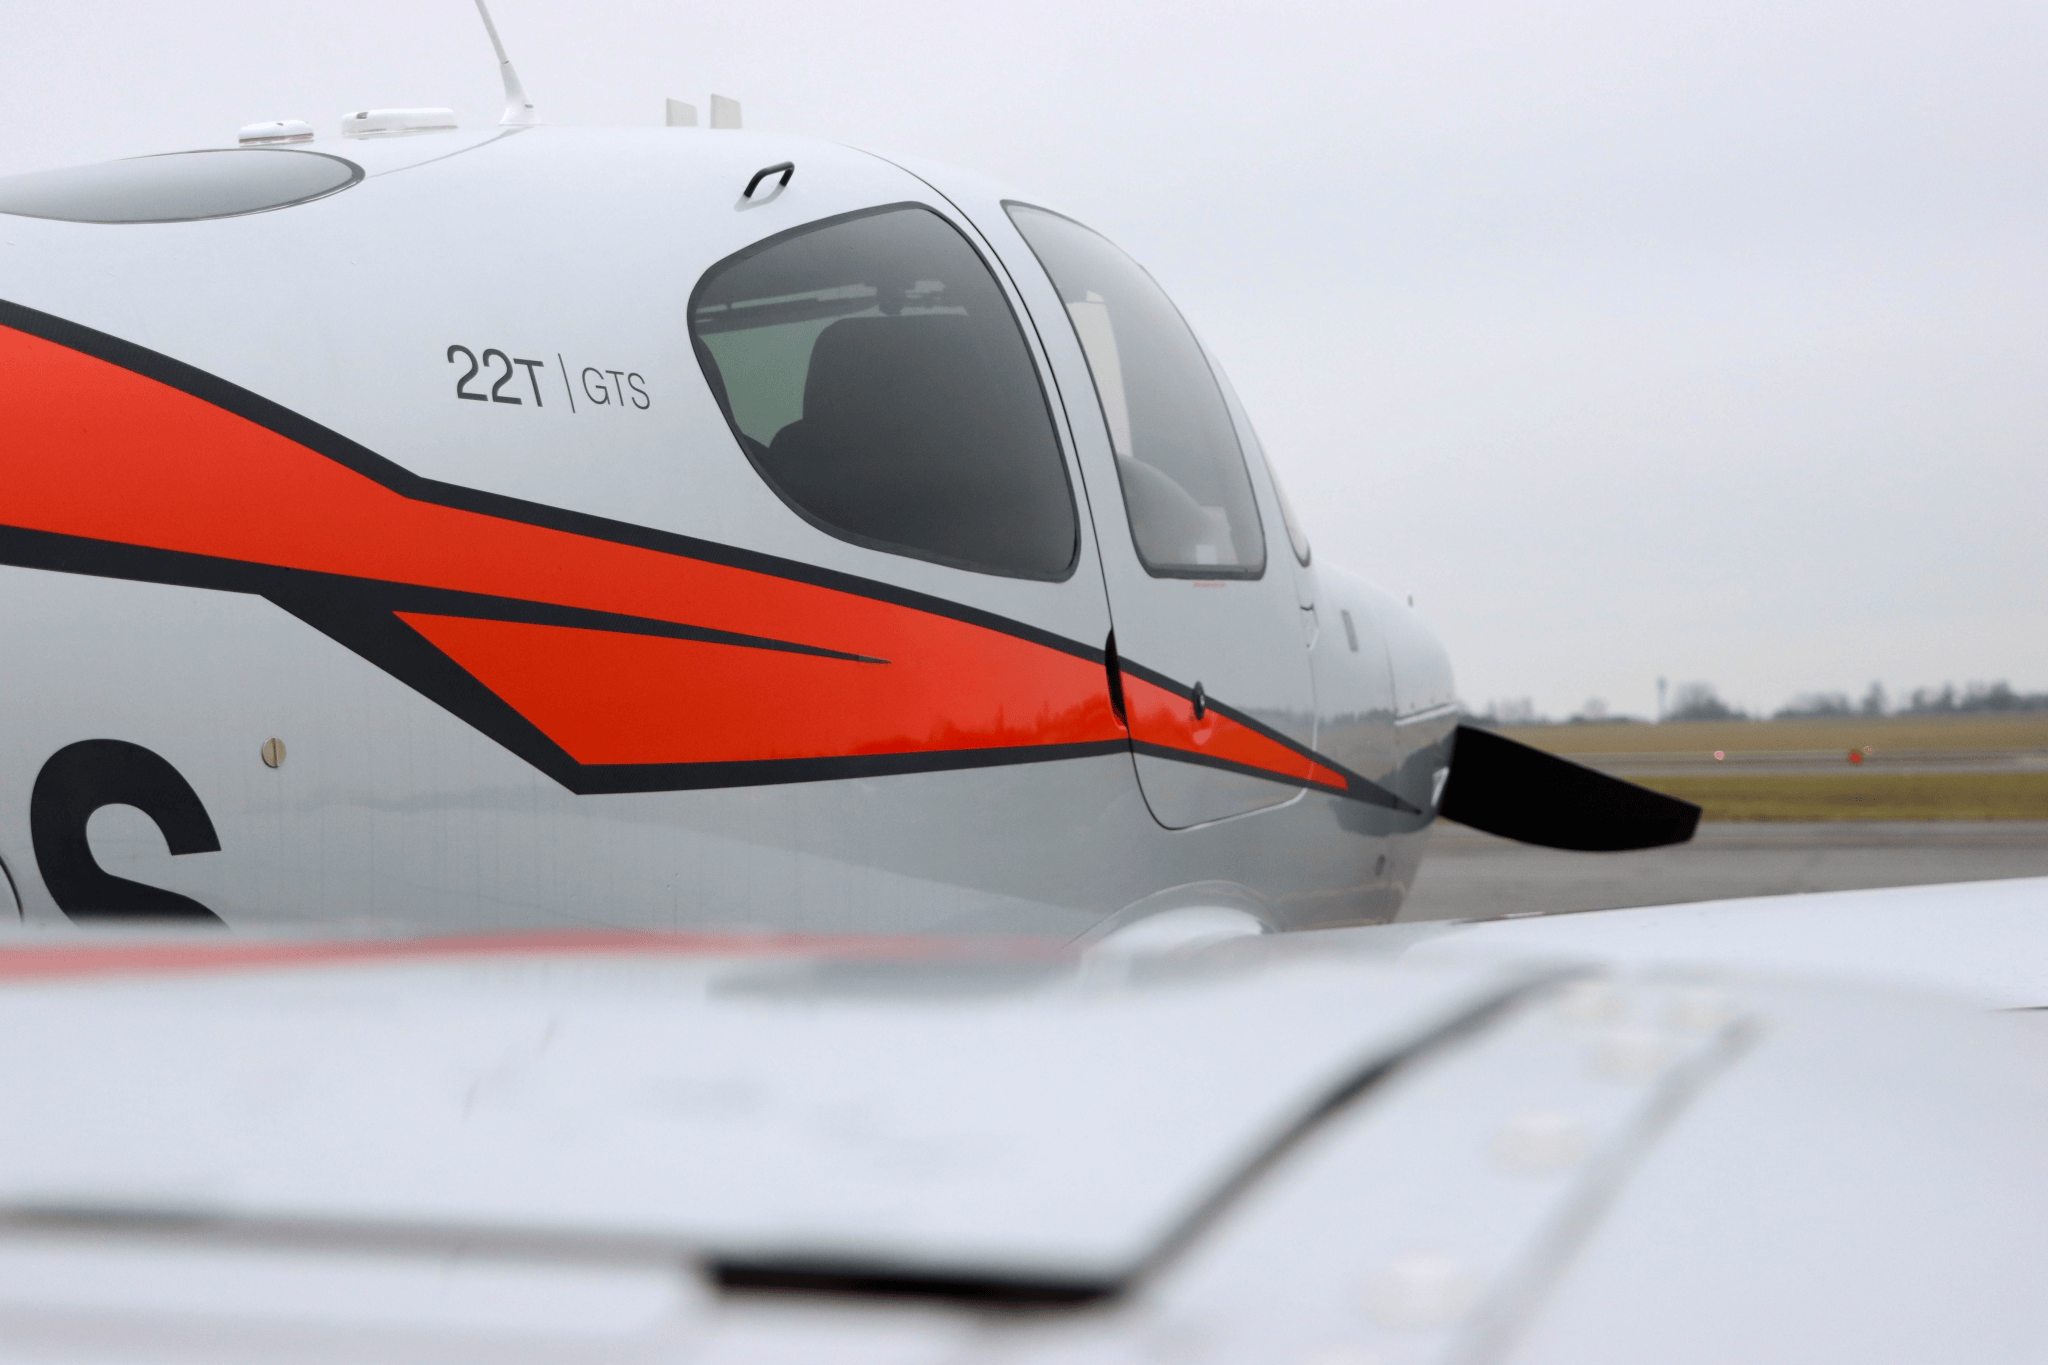
Cirrus Aircraft disclosed a data breach involving personal, financial and medical information after a social engineering incident compromised company documents in July.
The Duluth, Minnesota-based aircraft manufacturer said the incident occurred July 17, 2026, and resulted in the unauthorized disclosure of documents to an unknown third party. Cirrus notified state attorneys general on Nov. 10, according to breach disclosures reviewed by Claim Depot.
Information potentially exposed includes names, addresses, Social Security numbers, driver’s license numbers, passport and other government identification numbers, financial account information and medical records.
The company said it launched an investigation after discovering the incident and brought in outside forensic firms and other specialists to determine what information may have been affected. Cirrus said it also took steps to strengthen its security practices.
According to the Texas Attorney General filing, 280 Texas residents were affected. The filing lists 3,903 individuals affected overall. Separate disclosures were also made in Massachusetts and Vermont.
Cirrus said its investigation has not found evidence that the exposed information was used fraudulently. The company is offering affected individuals two years of complimentary credit monitoring through Epiq Universal Credit Monitoring.
Cirrus has not publicly detailed whether the affected records belonged to aircraft owners, employees or other individuals associated with the company.
0 replies